All case studies
FinPay: a DevSecOps pipeline to ship every day, securely
A CI/CD pipeline with security checks at every stage, zero-downtime Kubernetes deployments, secrets management and monitoring for a payment platform.
- Client
- FinPay
- Sector
- Banking & insurance
- production releases a week
- 46
- from commit to production
- 38 min
- uptime
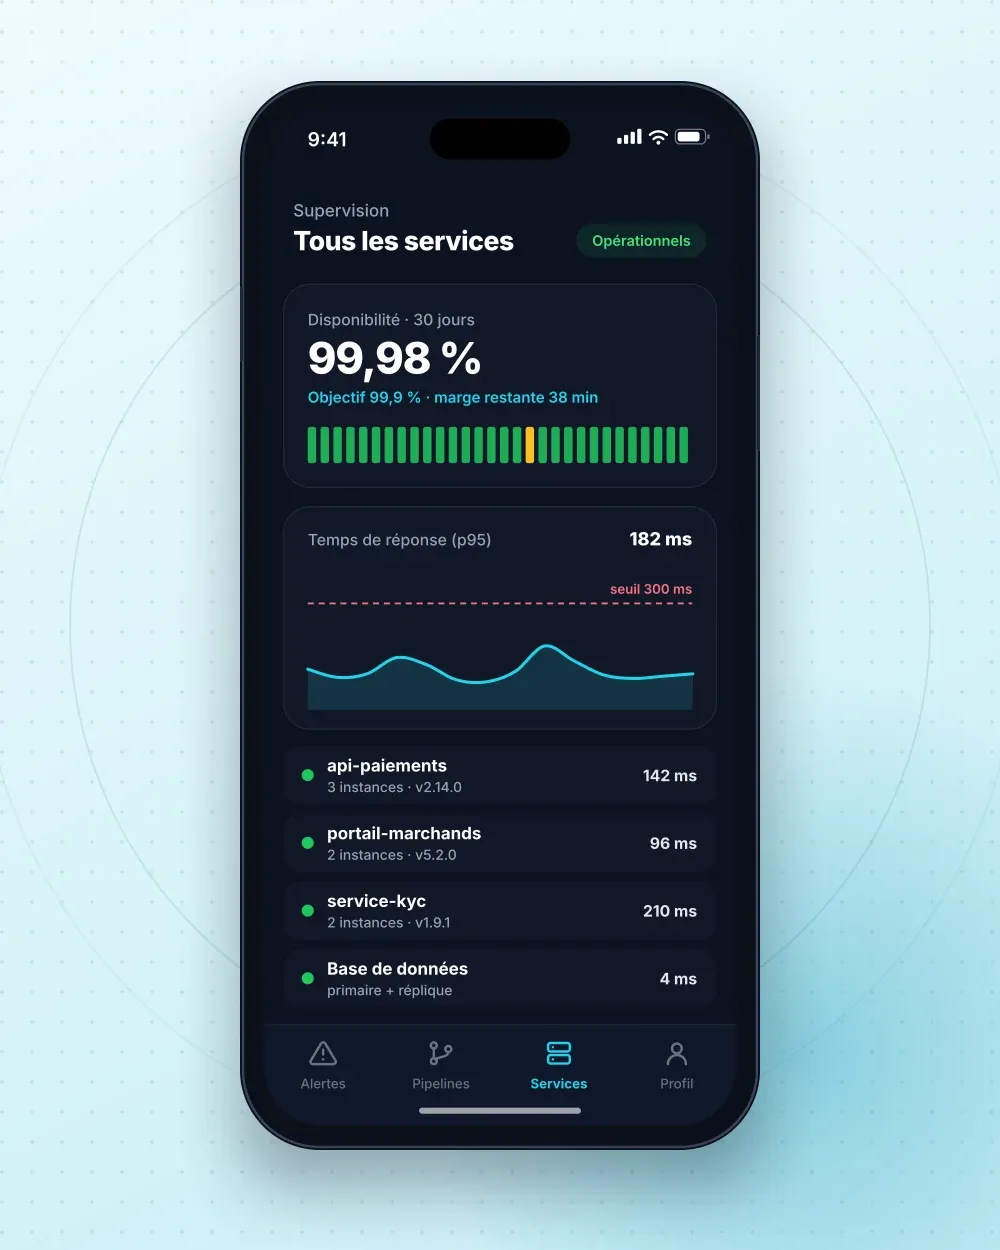
- 99.98%
Screenshots
The problem
FinPay released once a month, at the weekend, after a long list of manual checks. Security audits came at the end of the project and blocked releases.
- Rare, risky deployments
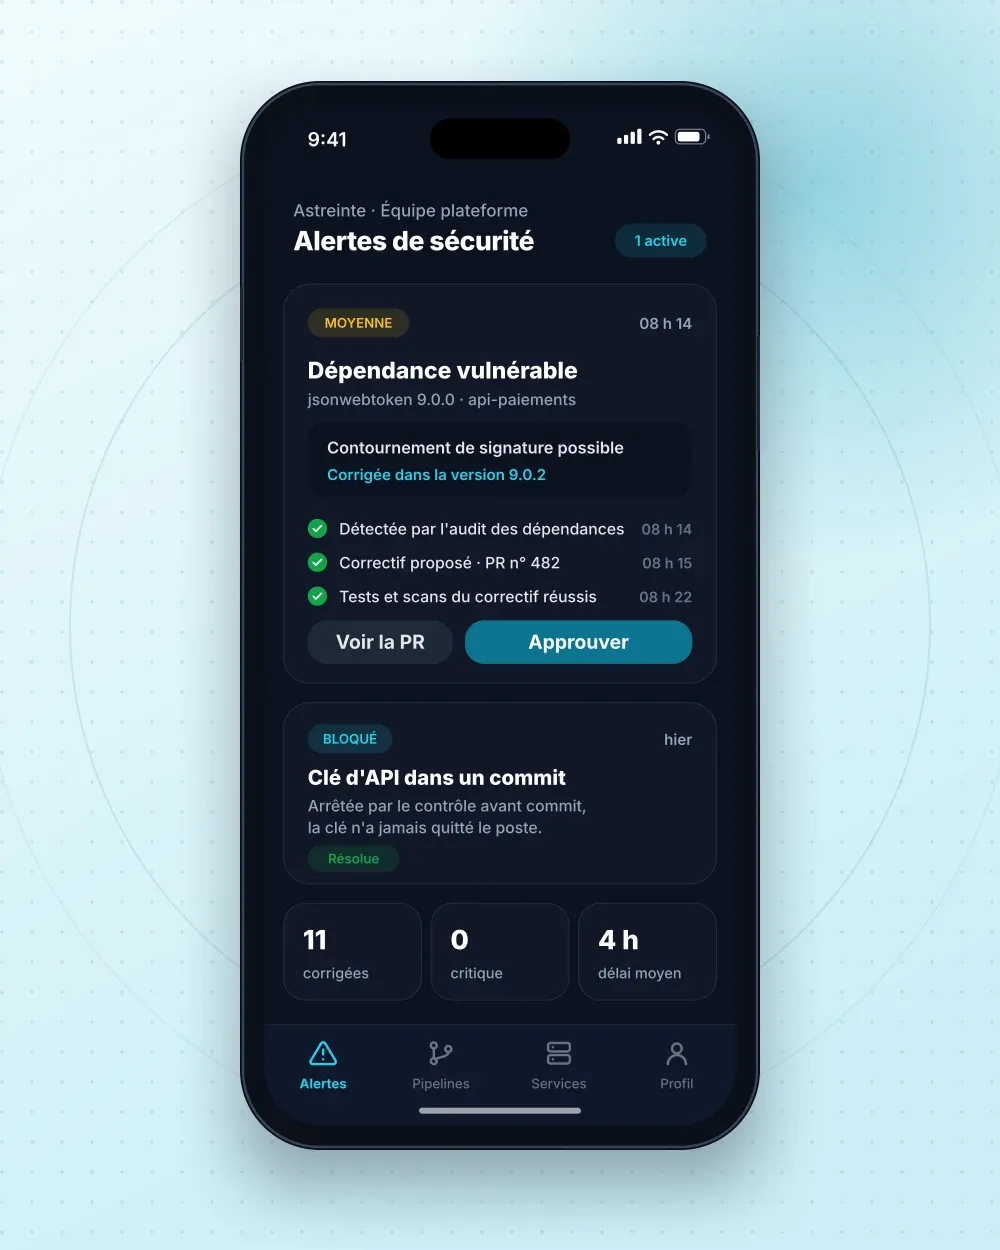
- Vulnerable dependencies found late
- Secrets shared in configuration files
The solution
We built a complete DevSecOps pipeline
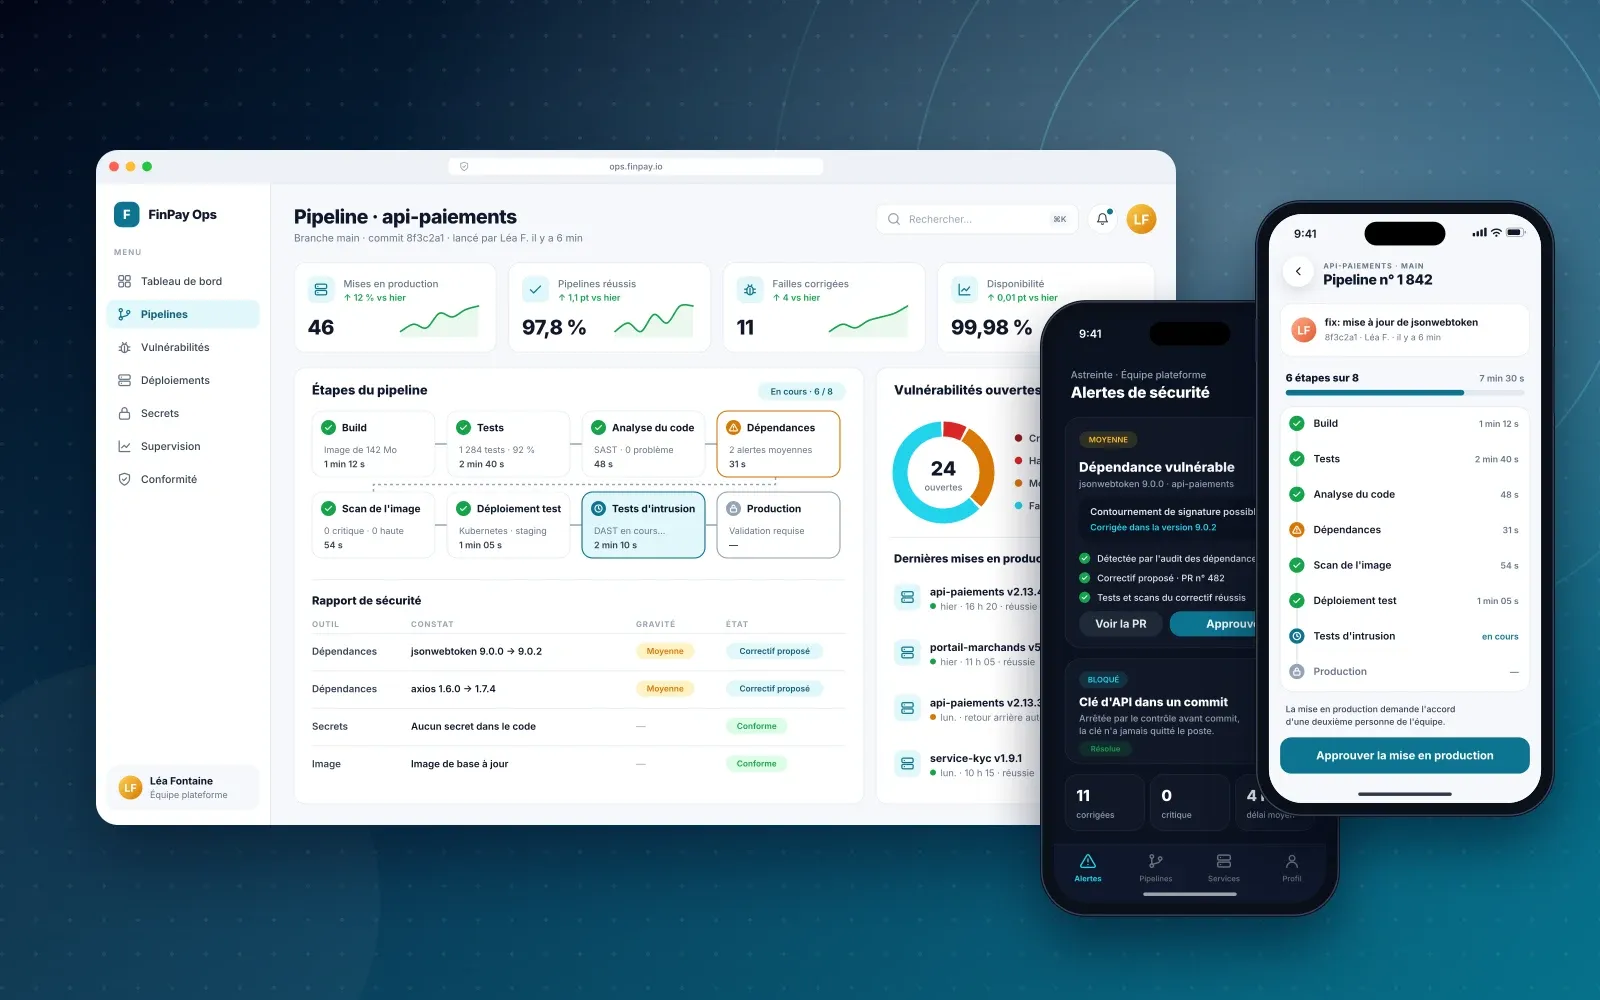
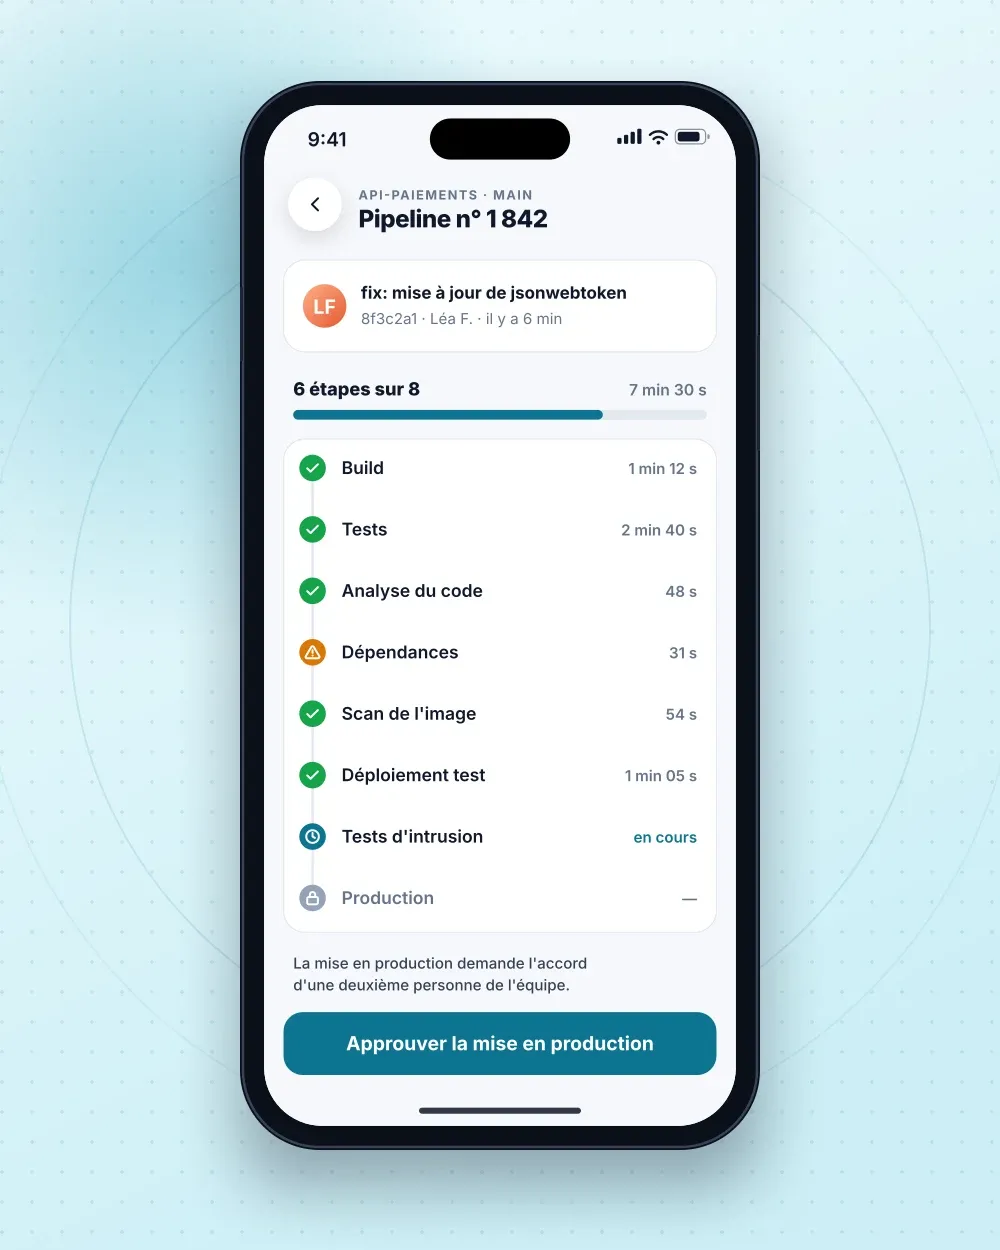
- CI/CD: build, tests, static code analysis (SAST), dependency audit, image scanning and automated penetration tests (DAST) on the staging environment
- Kubernetes deployment with automatic rollback when metrics degrade, and two-person approval for production
- Secrets in a dedicated vault, with a pre-commit check that blocks any key in the code
- Monitoring, alerting and uptime dashboards
Developers were trained in secure coding practices and in reading the reports.
The outcome
FinPay now releases several times a day, vulnerabilities are fixed in hours instead of weeks and every deployment leaves an audit trail for compliance reviews.
Facing a similar challenge?
Tell us about your situation: an engineer will reply within one business day.